If you're asking why does my website keep getting hacked, the answer is usually not that malware showed up. That's the symptom. The real problem is that nobody owns the site closely enough to notice what changed, what got installed, or where the alerts went.
A client called me after his website was offline for sometime over at name.com. Twelve years old, and it held decades of columns he'd written for trade publications. One morning it was a suspension notice from his host. His webmaster had stopped answering. He didn't know who to call or whether his work was gone. The panic isn't technical. It's personal.
The suspension notice that explained nothing
The host's email said the account had been filled with exploits and malware. That was the whole explanation. No filenames, no dates, no clue whether the problem was one file or fifty.
Then it offered a one time courtesy unsuspension if he agreed to change every password and clean up the account himself. If your only involvement with your website is logging in to post, that isn't advice. It's a liability handoff. He forwarded it to me weeks later still not knowing what it meant. That's normal. Hosting notices get written like legal disclaimers, not explanations.
A malware alert without context is not a diagnosis. It's a warning light on the dashboard. People waste time solving the wrong problem because of it.
He thought decades of work was gone
His actual fear was that thirty years of writing had disappeared. That was reasonable. Suspended accounts do get purged eventually. The good news took about ten minutes to confirm: nothing had been deleted. The files were exactly where they had always been. The site was stuck behind a wall he had no way through.
A site can be unavailable without being destroyed. But if you don't control the hosting, the admin login, or the email on the account, those feel identical from where you're standing.
The malware was already gone before I got there
By the time I had access, the host's scanner had found the malicious files and emptied them six weeks earlier. Two plugin folders were still on the server, but they were empty shells. If I had run another scan and trusted the result, I'd have gotten a clean report and learned nothing.
The evidence was in the PHP error log. 967 entries from one week in December where a plugin named hseo repeatedly contacted a command and control server asking what to do next. That log had been sitting there for nine months. Nobody had read it.
The plugin list had 21 active plugins and nobody had reviewed it in years. Two were fake. hseo was one. The other was wp-helper-70a4e6, a believable WordPress style name plus random characters so it blends into the list.
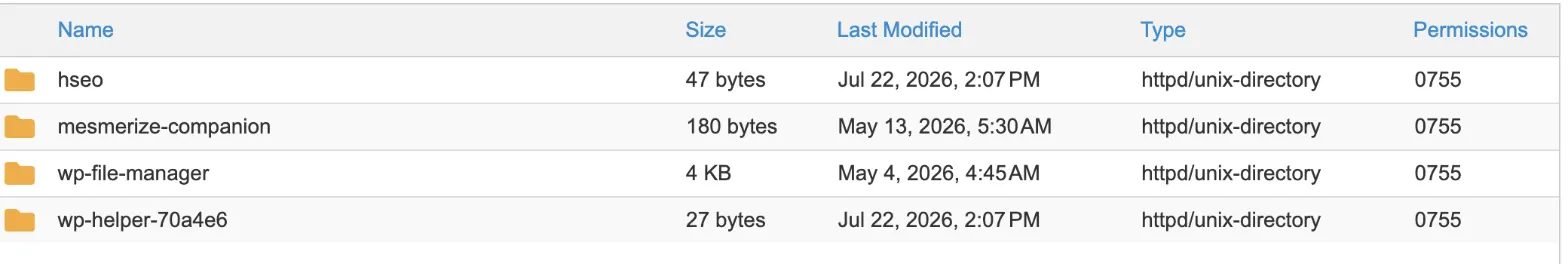
Neither jumps off the screen unless someone is looking. Notice the timestamps: both fake plugins were emptied at the same minute by an automated scanner, and nobody saw the report.
Here's the detail that stuck with me. wp-helper was still marked active in the database after its code had been deleted. The site was booting up every day trying to load something that no longer existed.
Plugins are not evil. But every plugin is another dependency, and dependencies need someone keeping an eye on them. If your site depends on 21 outside tools, you're depending on 21 separate update cycles and security histories. If someone is actively watching that, fine. If nobody is, a simpler build is the smarter choice.
The thing that actually worried me
The malware was bad. This was worse. In the web root sat a file called .tmb.zip, 351 MB, created in August 2025. A complete backup of the entire site, publicly downloadable by anyone who guessed the filename. I tested it. The server handed it right over. Inside was the configuration file with the database password in plain text.
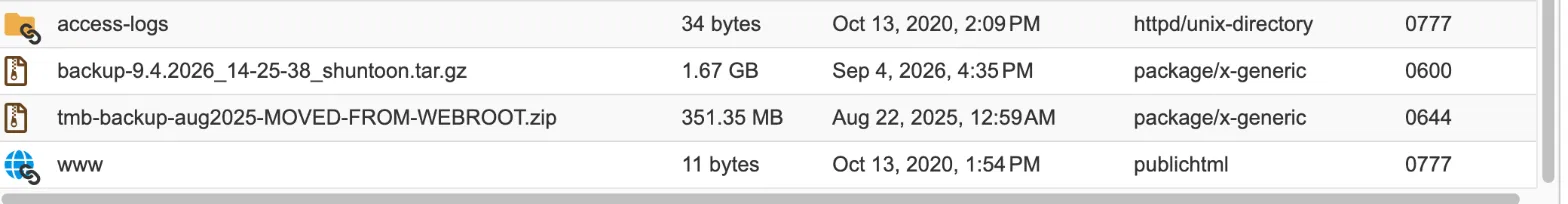
It had been sitting on the open web for about a year. Nobody knew it existed. It was almost certainly created by accident by a file manager plugin, which is how this usually happens. Not a movie hacker. Just clutter nobody cleaned up. Don't only ask whether your site was hacked. Ask what else is exposed because nobody has been checking.
The admin account belonged to someone else
There was exactly one user on the site: admin, registered in 2021. The email on it was a personal Gmail belonging to a developer my client had hired years earlier. Password resets went to that address, not to my client.
Then I pulled the login history. Every login from 2023 through 2025 came from overseas mobile carrier IP ranges. That wasn't a dramatic reveal. It was almost certainly the developer doing his job. But that's the point. A third party held the only working admin access, and when he stopped answering there was no path back in.
A business pays to have a site built, assumes the setup details are temporary, and years later finds the domain, hosting, admin account, and recovery emails all point somewhere else.
A hack is usually an ownership problem first
This is not a story about WordPress being bad software. WordPress runs a huge part of the web and runs it fine. What happened here is that a site had 21 active plugins, years of neglect, alerts going to an inbox nobody monitored, an error log full of evidence nobody read, a public backup sitting in the open, and no single person responsible for any of it. Every problem traced back to the same gap. Nobody was in charge.
So if you're wondering why does my website keep getting hacked, that's the question I'd ask first. Not who paid for it. Who actually checks the updates, the user accounts, the logs, the backups, the plugin list, the alert emails. If the answer is nobody, the fix isn't cleaning malware. It's assigning responsibility, or reducing complexity so there's less to manage.
Three things worth checking today
Each of these takes a couple of minutes.
That last one is the whole article in one sentence.
If nobody would notice, nobody would know what broke, and nobody has clear responsibility, the site is exposed before any attacker shows up.
If you want a second set of eyes on it, reach out. I can usually tell pretty quickly whether you have a malware problem, an access problem, or an ownership problem pretending to be both.